Cloud Security
Hands-on course on cloud-native security, from Linux container internals and Docker isolation to secure images, CI/CD pipelines, runtime hardening, and Kubernetes security. Learners identify weak configurations and apply practical security controls across the stack.
Course offered by
Instructors

Carlo Ramponi
Researcher

Luigi Dell'Eva
Researcher
Language
English
Subtitles: English, Italiano
Learning Objectives
- Explain how Linux namespaces, cgroups, filesystems, networking, and container runtimes are combined to implement Docker containers.
- Analyse container configurations and identify weak or unnecessarily exposed isolation boundaries.
- Apply Linux and Docker security mechanisms such as capabilities, seccomp, LSM policies, non-root execution, resource restrictions, and safer filesystem and device configurations.
- Assess container images and build pipelines for insecure Dockerfiles, vulnerable dependencies, exposed secrets, excessive software, and supply-chain risks, and integrate appropriate checks into CI/CD workflows.
- Explain the Kubernetes architecture and security model, including ServiceAccounts, RBAC, secrets, workload privileges, admission controls, and network exposure.
- Analyse Kubernetes workloads and cluster configurations to identify privilege-escalation paths and apply defence-in-depth hardening across containers, images, runtimes, and orchestration.
Prerequisites
- Basic understanding of cloud computing concepts, including IaaS and PaaS models. Familiarity with networking fundamentals, Linux command-line usage, basic scripting such as Python, and general cybersecurity principles is recommended.
Topics dealt with
Offensive SecuritySecure Development
Modules
Build your expertise
This course is part of the following learning pathways: Secure Software & DevSecOps, Penetration Tester
Cybersecurity skills are not built in a single session. Following a structured learning pathway helps you develop a complete and consistent skill set: step by step, at your own pace.
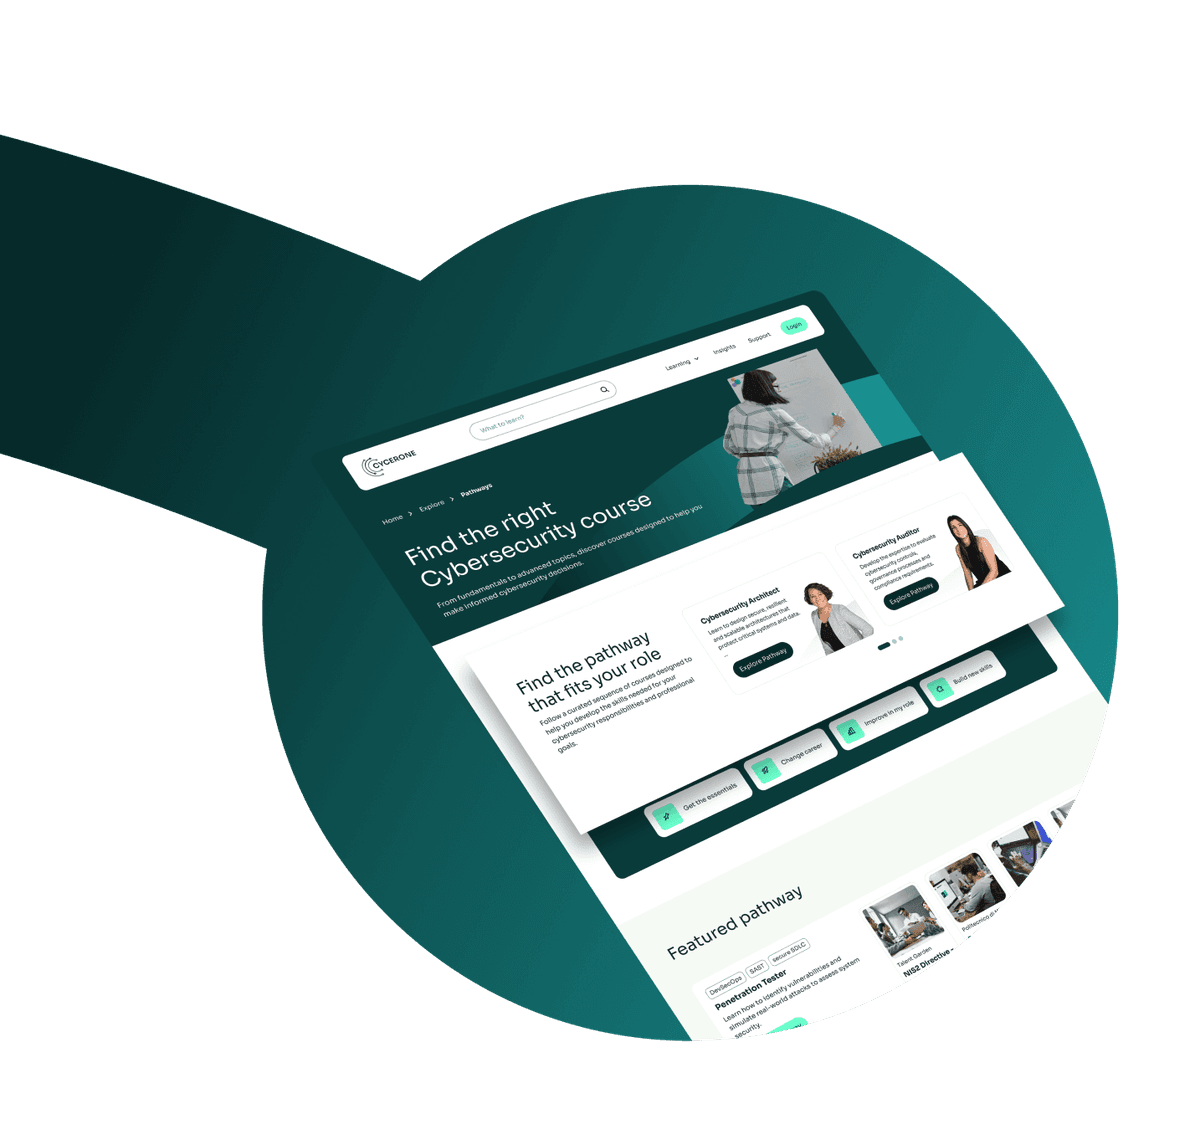
Not sure where to start?
Learn how the Cycerone portal works, how courses and learning pathways are organized, and how to find the training opportunities that best match your needs.